Findings
Severity and scoring
How severity and scores are decided.
Each finding carries a severity and, where it applies, a CVSS score and an OWASP WSTG mapping.
Severity levels
- Critical — exploitable now with serious impact. Fix first.
- High — significant impact; schedule promptly.
- Medium — real, but limited by conditions or impact.
- Low — minor exposure or defence-in-depth.
- Info — worth knowing, not a vulnerability on its own.
Severity feeds saved views such as Critical and high and the severity breakdown on every scan.
CVSS
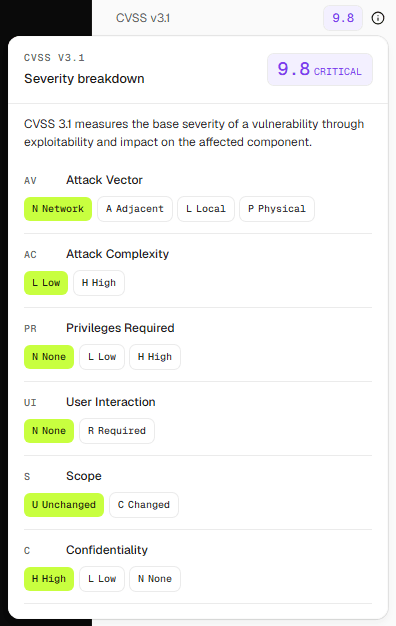
Findings are scored with CVSS 3.1 or 4.0. The workspace picks one in Settings → General (3.1 by default), so every finding shares the same scale. Open the score on a finding to see its vector broken down metric by metric.
WSTG
Web findings carry an OWASP Web Security Testing Guide test id. Filter the findings list by Weakness to see everything under one test, or read Most common weaknesses on the dashboard for the ranking across the workspace. See Coverage.